Permissions
Specify who or what can access information and execute actions. Give each person or AI assistant authority appropriate to its role and responsibilities.
Put the rules for execution into the operating model itself. Goveryn governs the information AI can use, the actions it may take and the moments when a person must decide.
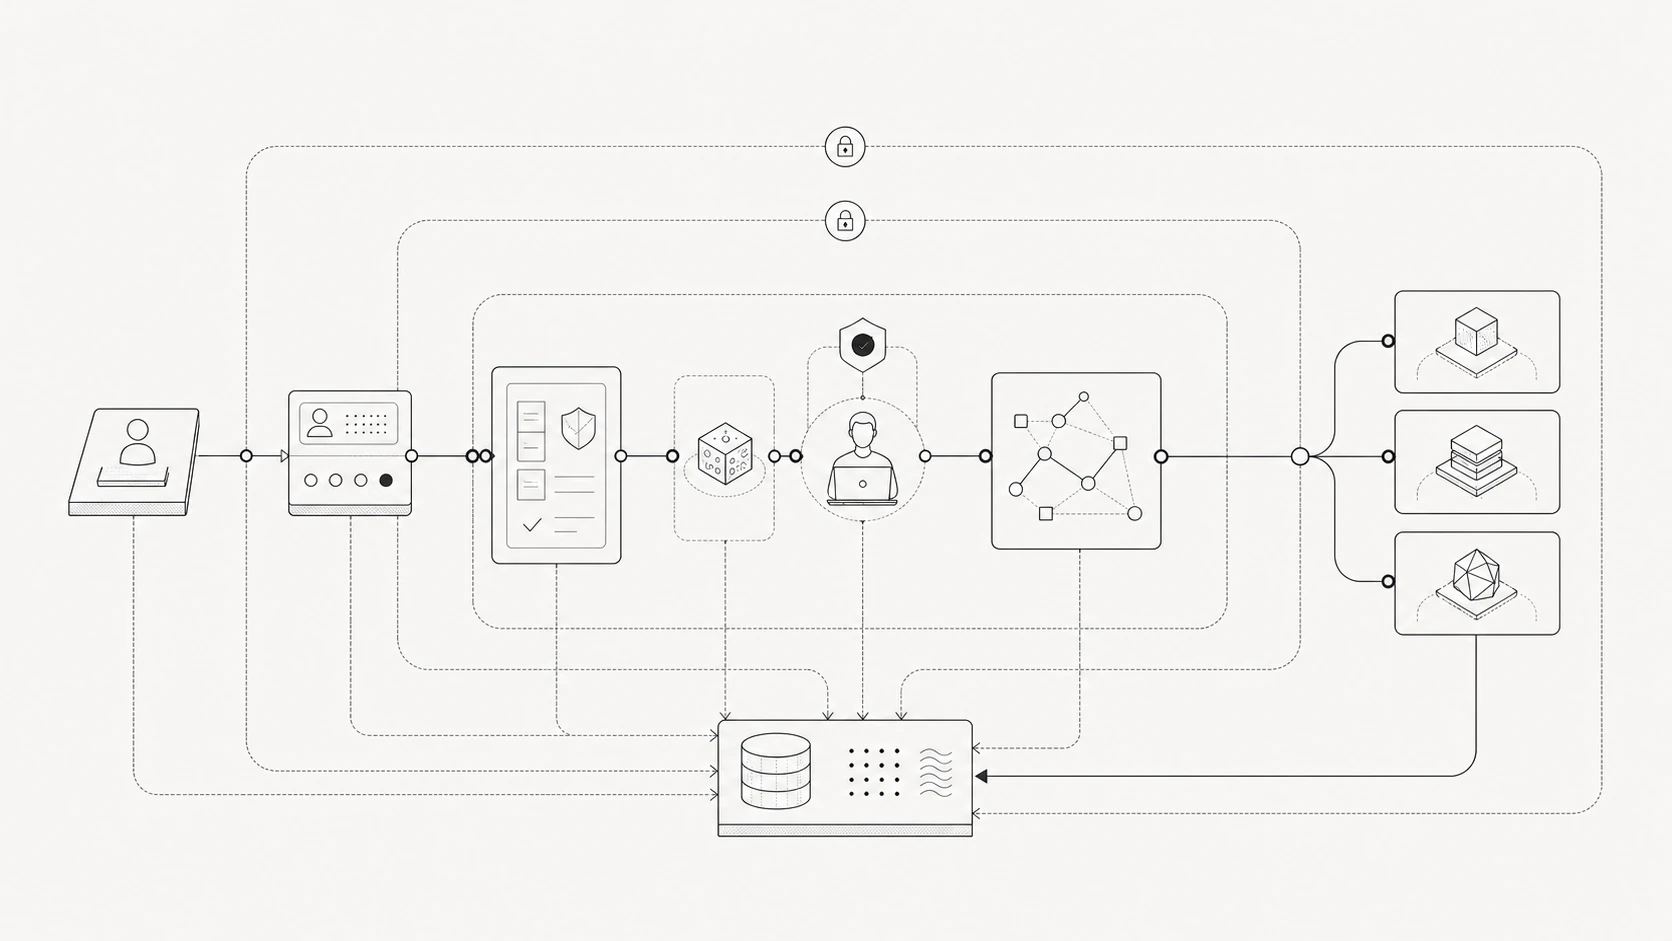
Define access, validation, human oversight, and traceability as part of execution. Choose a deployment architecture that reflects your data and operating requirements.
Specify who or what can access information and execute actions. Give each person or AI assistant authority appropriate to its role and responsibilities.
Check required inputs, business rules and execution conditions before a change proceeds. Make prerequisites part of the process.
Require a designated person to review an action at the steps you choose. Keep the proposed action, decision and resulting execution connected.
An unclear record, incomplete request or insufficient permission needs a defined response. Configure Goveryn to request information, assign a human task or escalate to the responsible owner.
Human participation can take different forms: supplying a missing value, reviewing a recommendation, approving a change or taking over an exception. The process makes that responsibility explicit.
Trace the records used, the operation requested, the person or assistant involved, approvals and execution status. Give operational and technical teams the context to investigate an exception and explain what happened.
Business owners define responsibilities, decision conditions and required reviews. IT and software teams connect systems and configure access and execution controls. Goveryn applies those definitions across applications, workflows and AI assistants.
Use a requirements discussion to work through your identity, integration, data-handling and deployment needs alongside the operating model.
You choose which actions require approval. AI can complete authorized routine work independently while designated decisions remain subject to review.
An action must satisfy its applicable permission, validation and approval requirements. Human approval is one part of the execution controls.
Keep the current status visible and route the issue according to the workflow. The responsible person can supply information, resolve an exception or decide the next authorized step.
Bring your business owner and technical team. Walk through the information, authority, approvals and execution history needed for a process you want to automate.